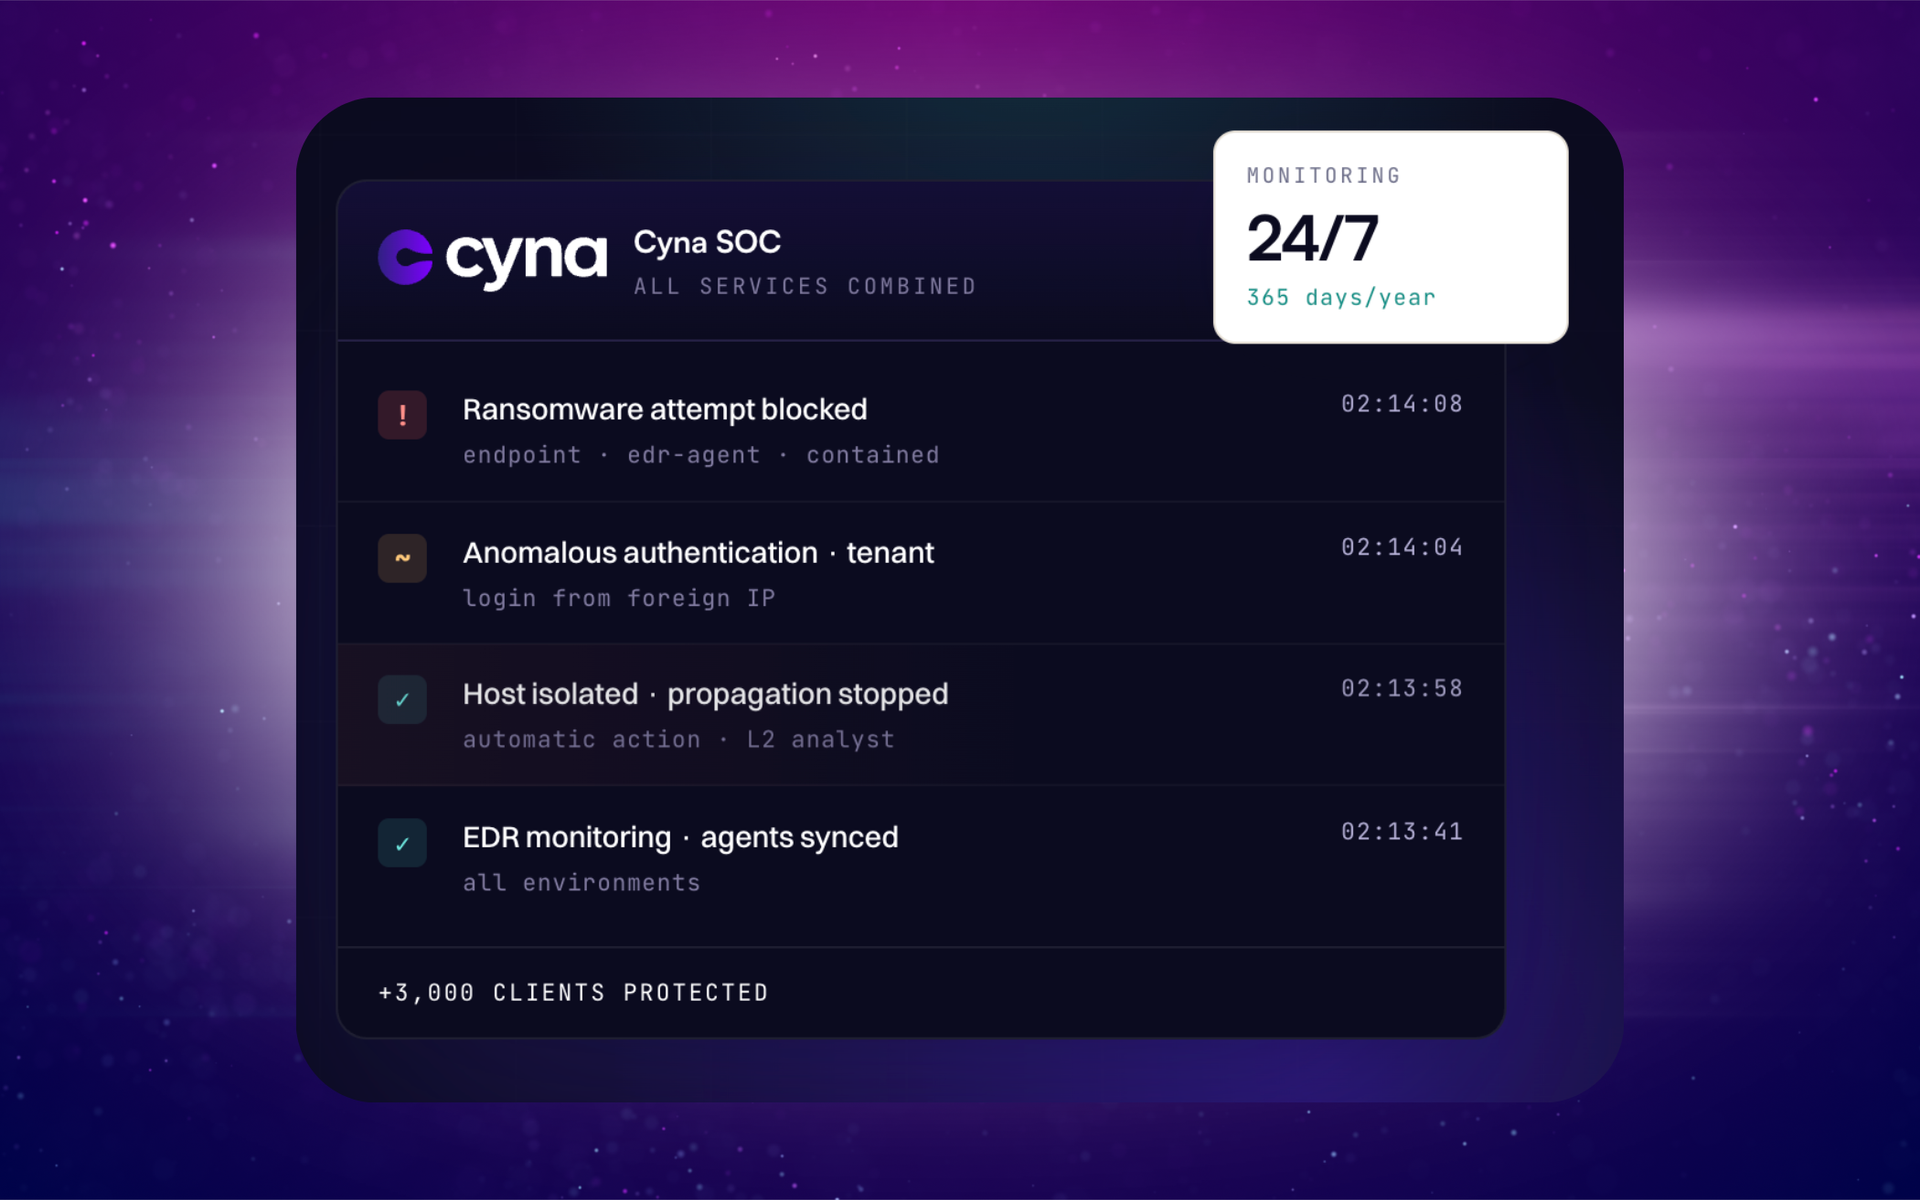
24/7 operated SOC
Human analysts monitor, triage and investigate alerts around the clock, including weekends and holidays.

 Thales Accelerate PartnerData, application and identity security, delivered by Cybergen.View the Thales page
Cyna operates a 24/7 managed security operations centre built around leading EDR technology, with human analysts who investigate, respond and call you when it matters. Cybergen brings it directly to your business.
Many organisations have endpoint detection and response tools but no one watching them around the clock. Cyna closes that gap with an operated SOC: analysts monitor, investigate and respond to alerts day and night.
Cybergen delivers Cyna's managed SOC directly to organisations, with onboarding, EDR deployment or migration, and the backing of Cybergen's threat intelligence and incident response services.
See all our technology partnersWe understand your environment and goals before recommending any Cyna product.
Design, deployment and integration with the tools you already run.
Support, tuning and Cybergen's intelligence-led services long after go-live.
The Cyna capabilities Cybergen can assess, supply, implement and support.
Human analysts monitor, triage and investigate alerts around the clock, including weekends and holidays.
Built on SentinelOne or Microsoft Defender. If you do not have an EDR, one is included, and migration from another EDR is supported.
Coverage across endpoints, servers, email, identity, network and cloud sources through SIEM collection.
SOAR automation contains common threats quickly, with analysts handling the rest.
An in-house incident response team is included by default, with no separate quote when an attack happens.
One console for emergency contacts, vulnerabilities and monthly reports.
An example ransomware attempt, stopped by Cyna with Cybergen support. Timings are illustrative.
A process on a laptop starts encrypting files and contacts an unknown server.
The endpoint agent stops the process and isolates the device from the network.
An analyst reviews the attack story, scope and root cause.
Malicious changes are reversed and the device is returned to service.
You receive a clear summary and recommendations to prevent a repeat.
Common reasons organisations choose Cyna, and the Cybergen service that goes with each.
Have your endpoints watched around the clock without hiring and retaining analysts.
24x7x365 MDRTurn existing SentinelOne or Microsoft Defender licences into an actively operated service.
Endpoint Detection & ResponseHave containment and incident response ready before you need it.
Incident ResponseFrom first conversation to long-term value, with one partner throughout.
 ArticleClosing the Detection Gap: How SMEs Can Access Enterprise-Grade SOC Protection Without an Enterprise BudgetCISOs are closing the SME detection gap without building a SOC from scratch. See the real cost of 24/7 monitoring vs. accessing enterprise-grade protection through Cybergen.
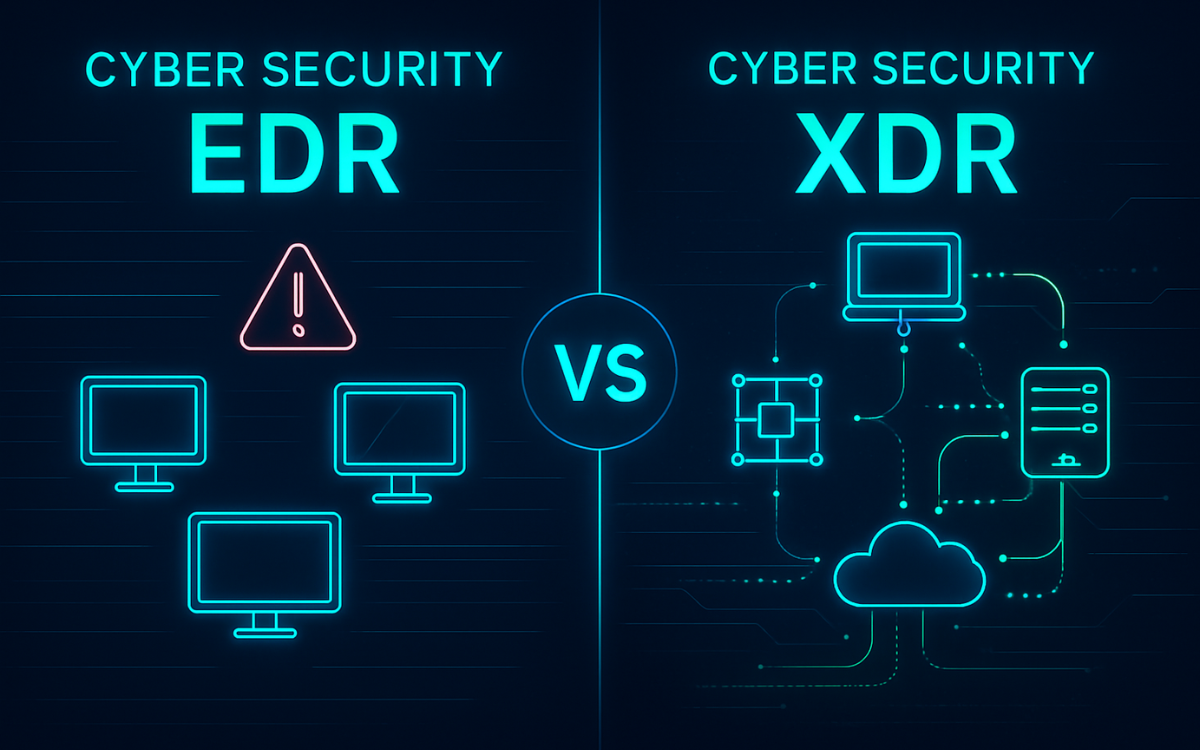 ArticleMDR vs. EDR: Which Cybersecurity Solution is Right for Your OrganisationExplore the key differences between MDR and EDR to determine which cybersecurity solution best fits your organisation’s needs. Compare features, benefits, and use cases to make an informed decision.
Cyna operates SentinelOne and Microsoft Defender. If you do not have an EDR, one is included, and migration from another EDR is supported.
Analysts investigate and respond directly, and contact you by phone when action is needed, rather than sending automated ticket emails.
Yes. Cyna's in-house CERT is included by default, so there is no separate quote during an attack.
Cybergen handles onboarding and EDR deployment, and adds threat intelligence, testing and incident response expertise around the service.
Tell us what you want to achieve and we will recommend the right Cyna products and services for you.
A member of our team will be in touch shortly.