

Threat Watch
The vulnerabilities attackers are exploiting right now, tracked live, alongside Cybergen analysis of the threats and threat actors targeting UK organisations.
Source: CISA Known Exploited Vulnerabilities catalogue. Catalogue version 2026.10.26.
What attackers are using right now
Every entry is a vulnerability with confirmed exploitation in the wild. Filter by your vendors to see what matters to you.
What to do with this list
- 1
Check your exposure
Search the feed for the vendors and products you run. Anything listed is being exploited in the wild, not just theoretically vulnerable.
Vulnerability Management - 2
Patch by real-world risk
Prioritise exploited vulnerabilities over raw CVSS scores. CISA sets federal deadlines for each entry, which make a sensible benchmark.
CTEM - 3
Hunt if you were exposed
If a listed system was internet-facing before you patched, look for signs of compromise rather than assuming you were missed.
Incident Response - 4
Validate, then repeat
Confirm fixes worked with targeted testing, and keep watching. New entries are added to the catalogue every week.
Penetration Testing
The groups we are tracking
Profiles from our threat intelligence team on the actors and malware behind attacks on UK organisations.
Scattered Spider
How one of the most notorious English-speaking crime groups talks its way past help desks and MFA, and what defenders can do about it.
Read the profile Callback phishing & data extortionSilent Ransom Group
Why law firms are in the firing line, how callback phishing leads to data theft and extortion, and how to protect your firm.
Read the profile Active and emerging operatorsRansomware groups
The ransomware operations shaping 2026: who is active, how their tactics are changing and what organisations can do to recover fast.
Read the profile Credential theft at scaleInfostealers
How infostealer malware harvests credentials and session cookies, and how stolen logins become the first step in larger attacks.
Read the profileLatest threat intelligence
 THREAT INTELLIGENCE3 October 2026STIX and TAXII Explained: Sharing Threat Intel at SpeedWhat are STIX and TAXII? Learn how these open standards structure and share cyber threat intelligence, and how your SOC can use them to detect threats faster.
 THREAT INTELLIGENCE2 October 2026How to Build a Cyber Threat Intelligence Program Your SOC Will Actually UseA practitioner's guide to building a cyber threat intelligence program: intelligence requirements, collection, analysis, SOC integration, metrics and a roadmap.
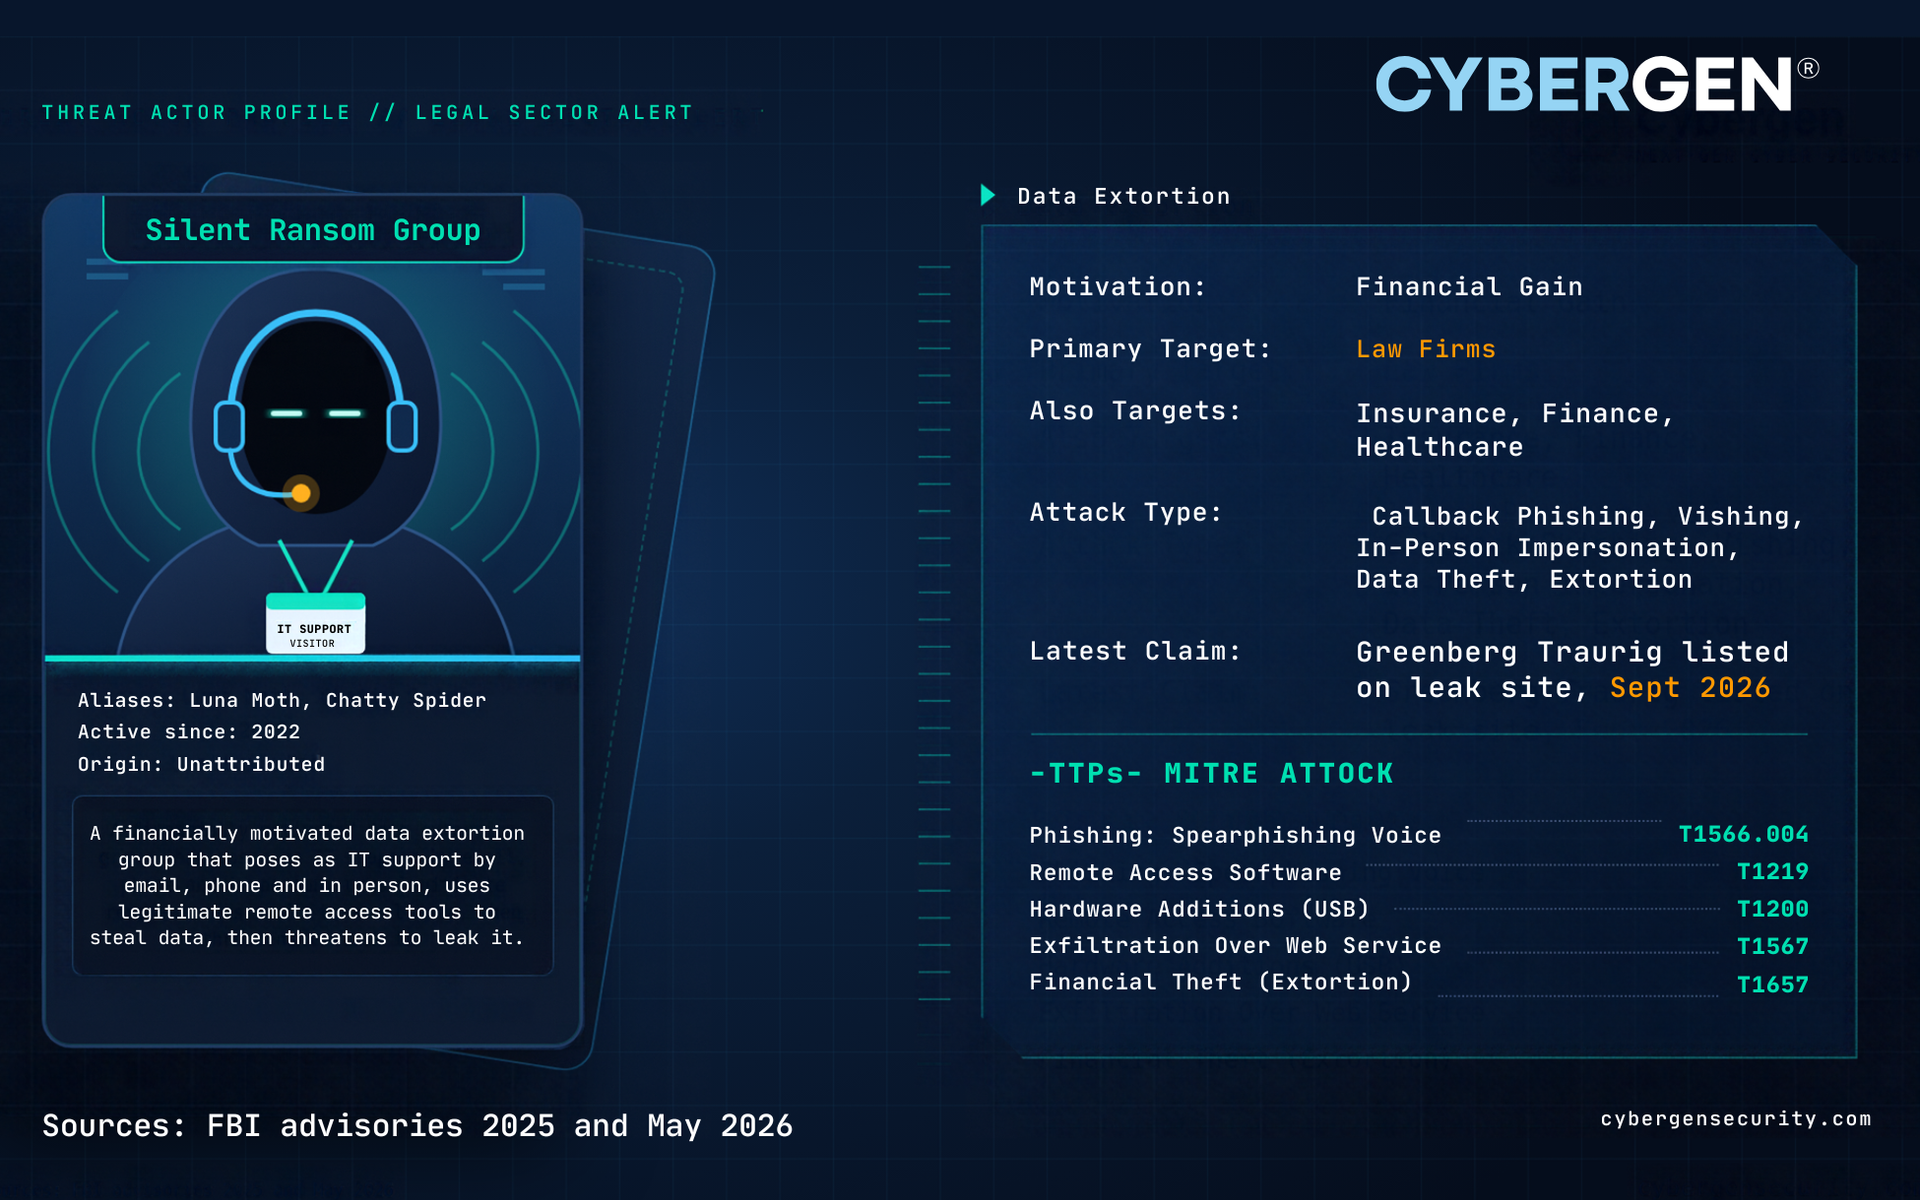 THREAT INTELLIGENCE28 September 2026Law Firms Are Under Attack: Inside the Silent Ransom Group ThreatGreenberg Traurig is the latest law firm hit as Silent Ransom Group targets the legal sector. Learn how these attacks work and how to protect your firm.
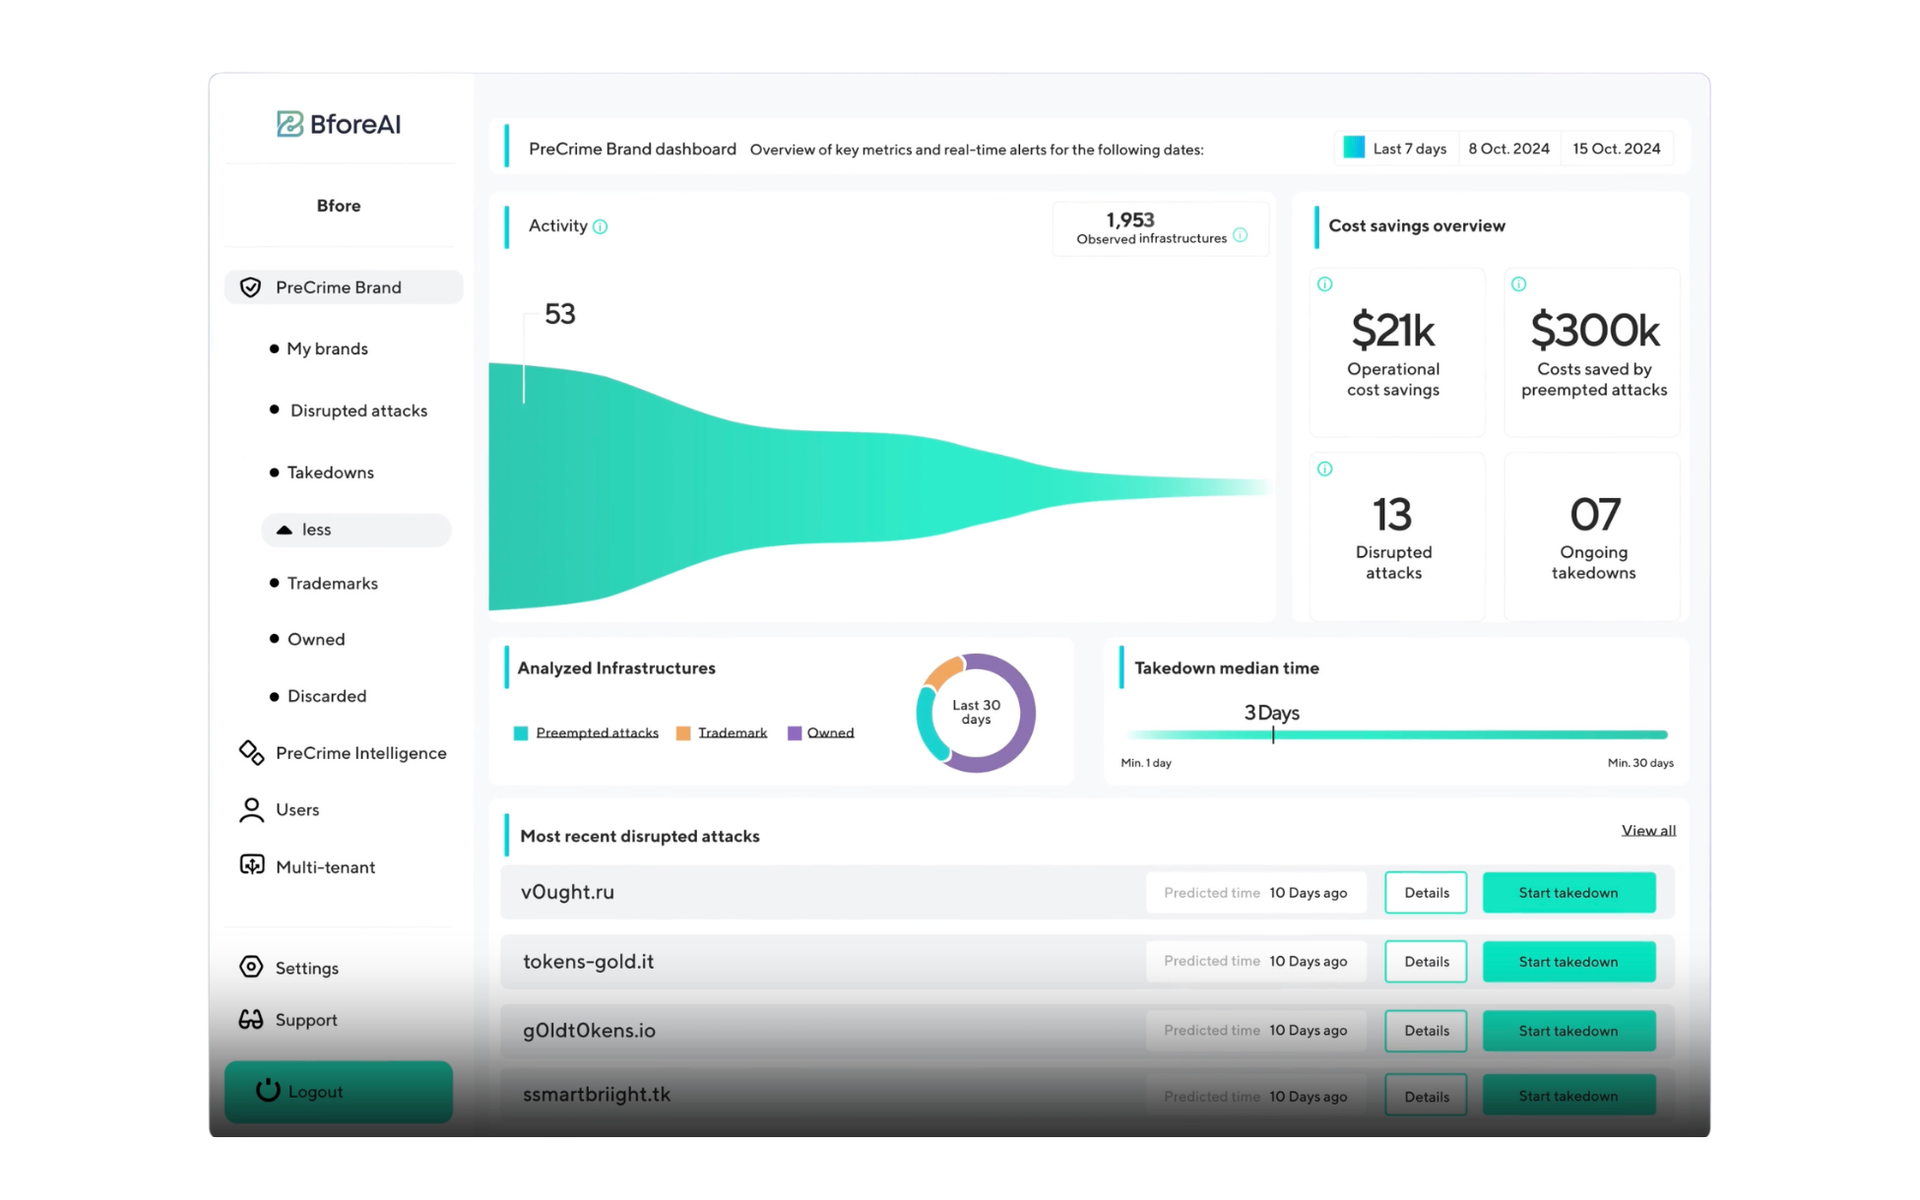 CYBER SECURITY NEWS18 September 2026The CISO's Guide to Automated Domain Takedown: How Predictive Cybersecurity Ends the Manual GrindManual phishing and domain takedown investigations cost security teams hundreds of hours a year. See how BforeAI's PreCrime™ predictive cybersecurity platform, available in the UK exclusively through Cybergen, detects and automates takedown of weaponized and impersonated domains before they cost you time or money.
 CYBER SECURITY NEWS2 September 2026The UK Cyber Security and Resilience Bill Just Reached Parliament: What Boards Need to Know Before the 24-Hour Reporting Clock StartsWhat UK boards need to know about the Cyber Security and Resilience Bill, including its scope, 24-hour reporting rule, penalties and compliance steps.
 CYBER SECURITY NEWS15 August 2026Cybersecurity for Critical Infrastructure: Why Resilience Matters More Than EverCritical infrastructure organisations face increasing cyber threats. Discover how Thales security solutions help improve resilience and protect essential services.
Get Threat Watch in your inbox
Our monthly threat intelligence briefing: the exploited vulnerabilities, campaigns and actors that matter, with what to do about them.