Member and Client Fraud
Criminals use stolen identities and account takeover to redirect pension transfers and withdrawals.

 Thales Accelerate PartnerData, application and identity security, delivered by Cybergen.View the Thales page
Pension schemes, administrators and wealth managers hold member data and move large sums. We help trustees and firms protect both and evidence it to regulators.
Pension schemes and wealth managers are prime targets for fraud and ransomware. They hold detailed personal and financial data on members and clients, and they rely heavily on administrators and technology suppliers.
Cybergen helps trustees, administrators and wealth firms understand their cyber risk, test their defences, monitor around the clock and meet the expectations of the Pensions Regulator, the FCA and DORA.
Criminals use stolen identities and account takeover to redirect pension transfers and withdrawals.
Most schemes outsource administration. A breach at one administrator can expose millions of members.
Disruption to payroll, administration and dealing systems stops payments and damages trust.
Attackers impersonate trustees, advisers and clients to authorise fraudulent payments.
Voice and video impersonation is making social engineering of finance and client teams more convincing.
The obligations that shape security in pensions & wealth management, and how we help you meet them with evidence rather than paperwork.
Trustees and scheme managers are expected to assess and manage cyber risk, including the risk posed by administrators and suppliers.
Official guidanceRegulated firms must identify important business services, set impact tolerances and prove they can stay within them.
Official guidanceFinancial entities in the EU must meet requirements for ICT risk management, incident reporting, resilience testing and third party risk.
Official guidanceMember and client data must be protected and qualifying breaches reported to the ICO.
Official guidanceHow a typical attack on pensions & wealth management unfolds, step by step. Press play to watch it run.
A member's email account is compromised through an infostealer on their home laptop.
Attackers log into the member portal and change contact and bank details.
A transfer to a fraudulent scheme is requested and supported by forged documents.
The money leaves before the member notices, leading to a complaint and regulatory scrutiny.
Threat intelligence flags the stolen credentials, portal testing hardens account change controls, MDR spots the unusual activity, and supplier assurance makes sure your administrator's controls match your risk.
Illustrative example, not a real incident.
DORA compliance requirements explained: who is in scope, the core obligations, how DORA compares with NIS2 and ISO 27001, and the steps to get ready.
Read article · 10 min
Threat-led penetration testing (TLPT) is now required under DORA and supports NIS2. Learn how TLPT differs from red teaming and standard pen testing.
Read article · 13 min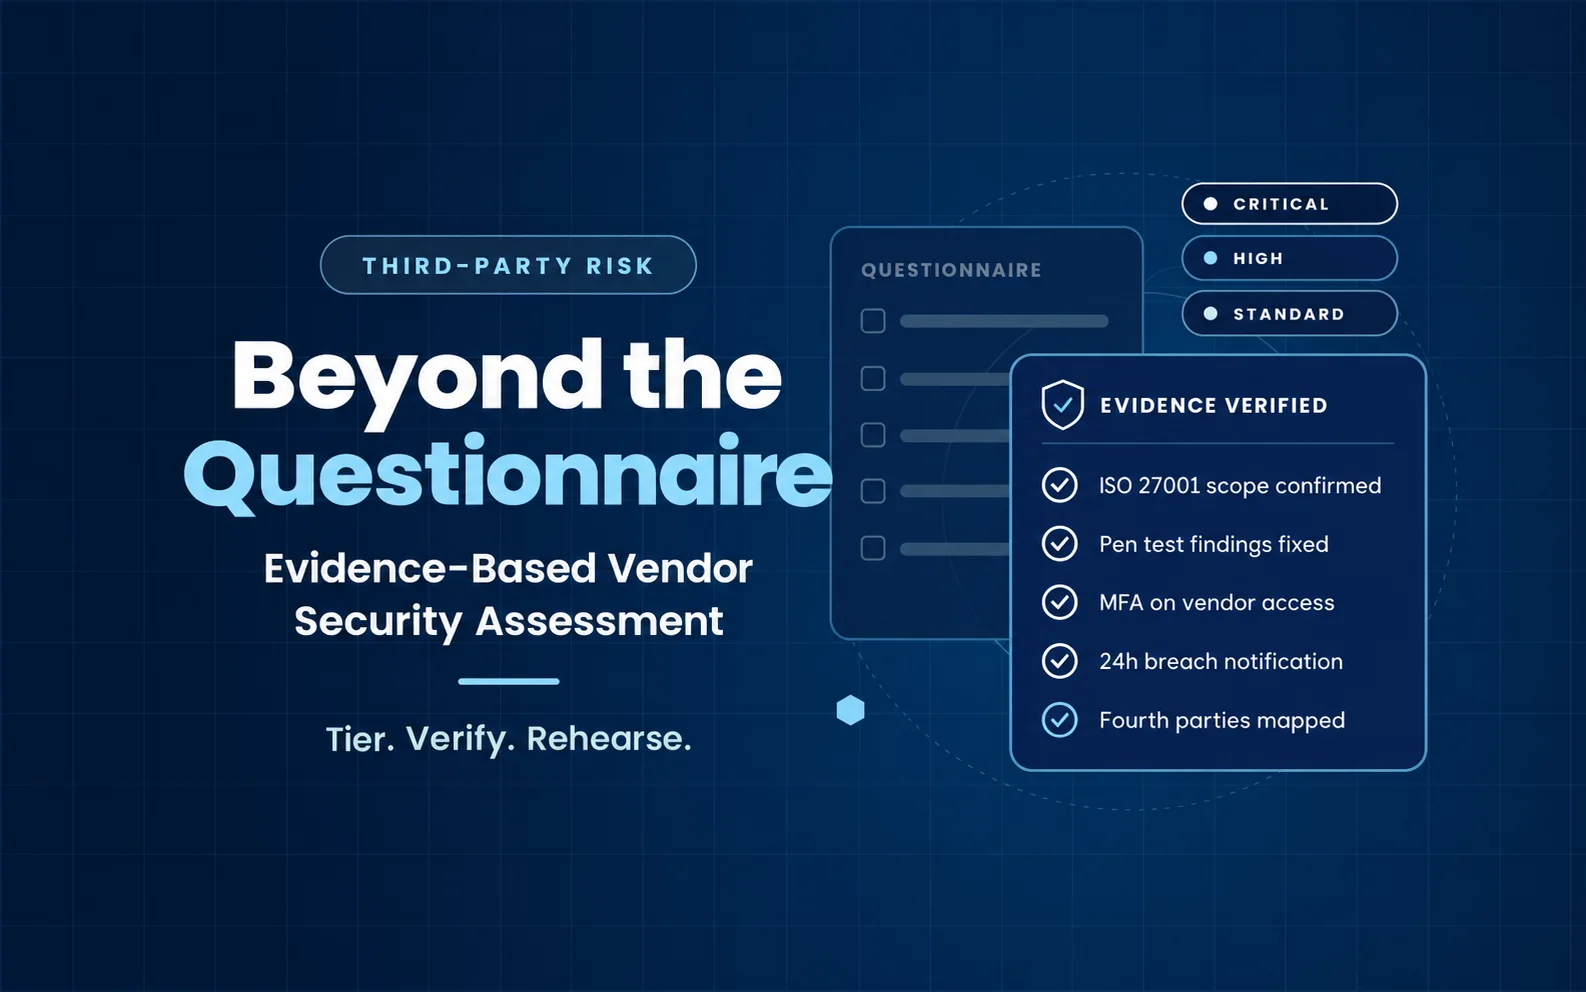
How to assess vendor security with evidence: tier suppliers by impact, validate controls and move to continuous third-party risk management.
Read article · 10 minUnderstand the risk to members and assets, make sure administrators and suppliers have appropriate controls, and have a tested incident plan. We help trustees do all three.
We review their controls, evidence and testing against your risk, rather than relying only on a questionnaire.
If you are an EU financial entity, or provide ICT services to one, it may. We help you work out your obligations and prepare.
Yes. We provide clear, non technical briefings on threats, risk and what good looks like.
Tell us about your organisation, the regulations you work under and what is worrying you most.
A member of our team will be in touch to talk through your sector and requirements.